Xiaomi has officially begun rolling out the September 2026 Android security patch to a diverse range of its devices, spanning the flagship Xiaomi series, the performance-driven POCO lineup, and the popular Redmi family. This major update, arriving as part of the HyperOS 4, addresses critical vulnerabilities within the Android framework, system architecture, and various vendor-specific hardware components.Here is a comprehensive breakdown of the devices receiving the update and the crucial security flaws it resolves.
Devices Receiving the September 2026 Update
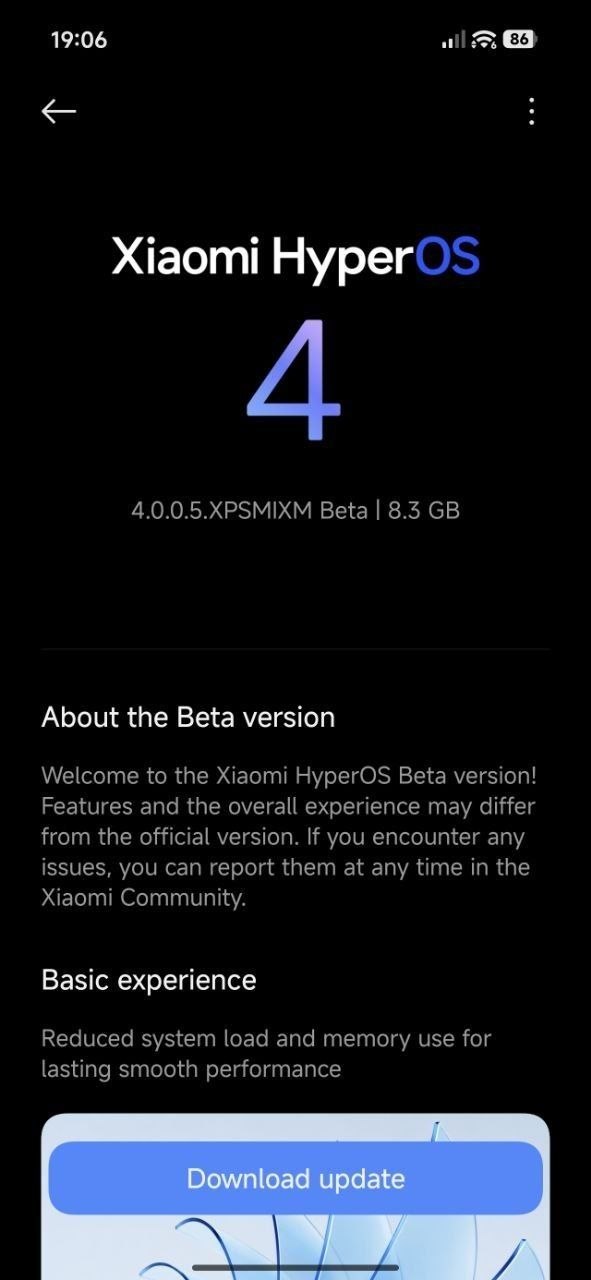
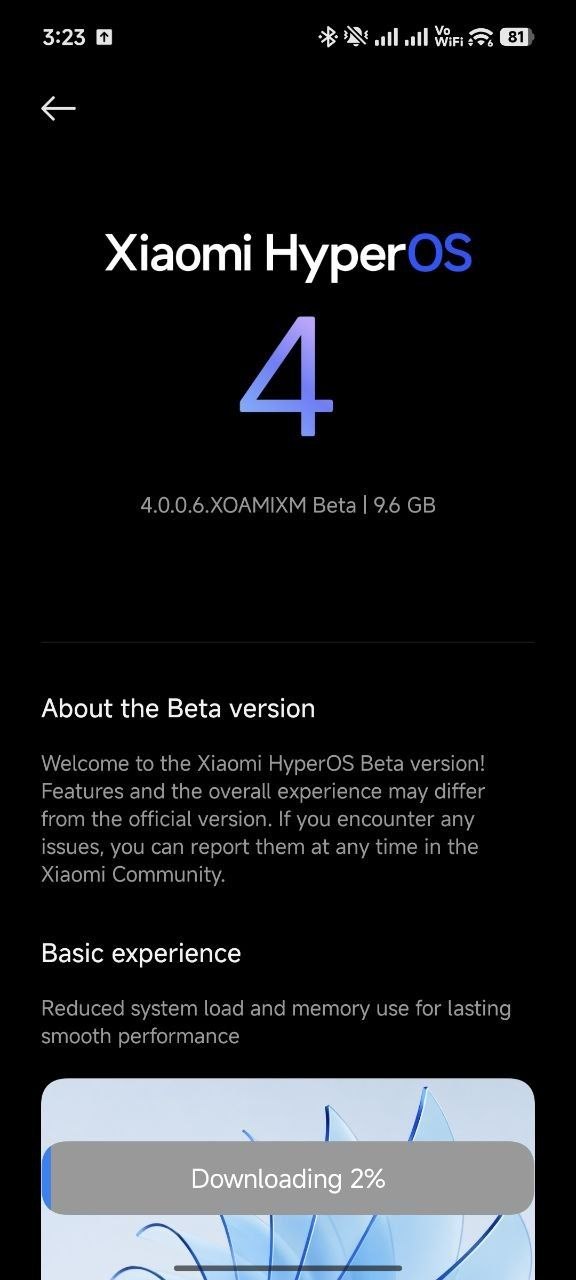
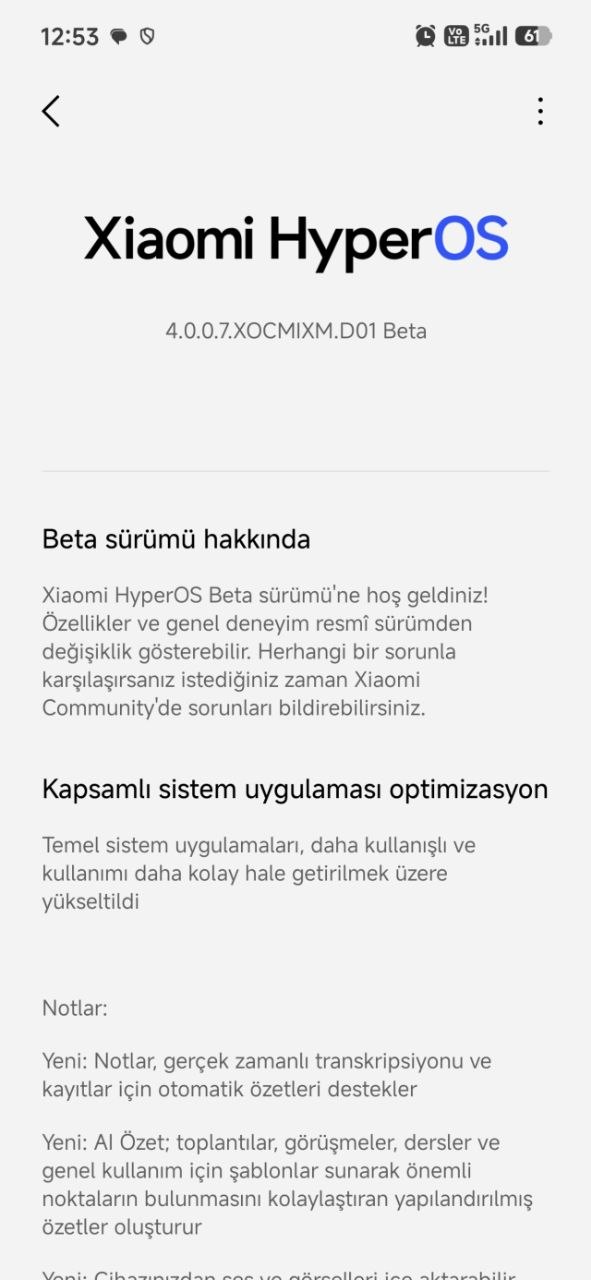
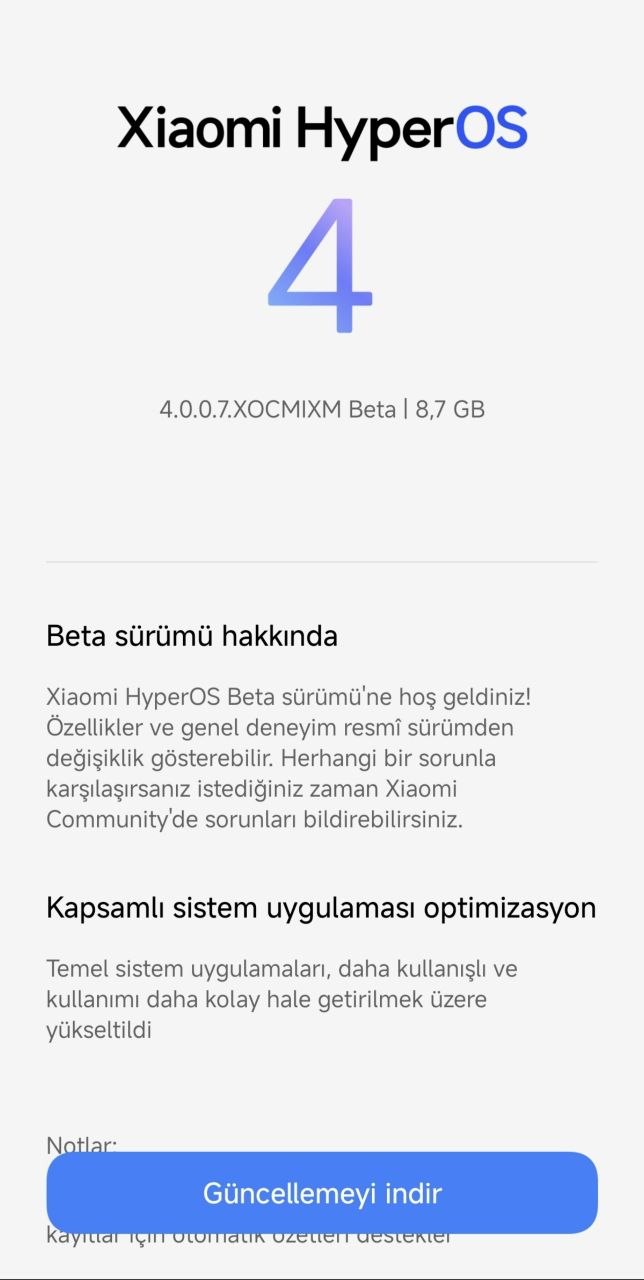
The initial rollout primarily targets devices in China, alongside key Global and EEA (European Economic Area) variants. If you own one of the following devices, the OTA (Over-The-Air) update should be reaching your device if you register HyperOS 4 Global open beta, September security patch for HyperOS 3 is still not received yet:
Xiaomi Series
- Xiaomi 15: Global (OS4.0.0.7.XOCMIXM) | EEA (OS4.0.0.9.XOCEUXM)
- Xiaomi 15 Ultra: Global (OS4.0.0.6.XOAMIXM) | EEA (OS4.0.0.6.XOAEUXM)
- Xiaomi 17T: EEA (OS4.0.0.7.XPTEUXM)
- Xiaomi 17T Pro: EEA (OS4.0.0.6.XPSEUXM)
- Xiaomi MIX FLIP 2: China (OS4.0.0.10.XOHCNXM)
- Xiaomi Pad 7S Pro 12.5: China (OS4.0.0.11.XOTCNXM)
Redmi Series
- REDMI K80: China (OS4.0.0.8.XOKCNXM)
- REDMI K80 Pro: China (OS4.0.0.8.XOMCNXM)
- REDMI K100 Pro Max: China (OS4.0.0.8.XGNCNXM)
POCO Series
- POCO F7 Pro: China (OS4.0.0.8.XOKCNXM)
- POCO F7 Ultra: China (OS4.0.0.8.XOMCNXM)
- POCO F9 Ultra: China (OS4.0.0.8.XGNCNXM)
What the September 2026 Security Patch Fixes
This month’s security bulletin is particularly massive, resolving dozens of severe vulnerabilities across both the Android Open Source Project (AOSP) foundation and closed-source vendor hardware.
1. Android Framework and System (Critical RCE and EoP Threats)
The most alarming vulnerabilities addressed in this patch are found within the Android Framework and System components.
- Remote Code Execution (RCE): The update patches multiple “Critical” RCE vulnerabilities (such as CVE-2026-28604, CVE-2026-28618, and CVE-2026-28639). These flaws are highly dangerous because they could allow a remote attacker to execute malicious code on the device without any user interaction or additional privileges.
- Elevation of Privilege (EoP): Several Framework vulnerabilities (e.g., CVE-2026-28666, CVE-2026-55273) were fixed. These bugs previously allowed malicious apps to silently elevate their system permissions, giving them unauthorized access to private data.
2. Kernel & Google Play System Updates
The update patches upstream Linux kernel vulnerabilities that could lead to privilege escalation within the Protected Kernel-Based Virtual Machine (pKVM) and NFC subsystems (e.g., CVE-2026-31629, CVE-2026-58846). Additionally, Project Mainline modules like Media Framework, Media Codecs, Wi-Fi, and Ultra-wideband (UWB) received targeted fixes via Google Play system updates to prevent Denial of Service (DoS) and RCE attacks.
3. Vendor-Specific Hardware Vulnerabilities
Because Android devices rely on hardware from various manufacturers, Xiaomi’s September patch includes mandatory fixes directly from chipset and GPU vendors:
- Qualcomm: Addressed a Critical vulnerability (CVE-2026-25289) in closed-source components, alongside several High-severity security issues affecting the core chipset environment.
- MediaTek: Patched multiple High-severity vulnerabilities affecting the Modem, HEVC Decoder, APU (AI Processing Unit), Trusted Memory, and Imaging components.
- ARM & Imagination Technologies: Fixed numerous High-severity flaws in ARM Mali GPUs (e.g., CVE-2026-0001) and PowerVR GPUs, securing the graphical rendering pipelines against memory corruption attacks.
- Unisoc & Tsingteng Micro: Resolved multiple modem vulnerabilities for Unisoc-powered devices and a StrongBox security module flaw provided by Tsingteng Micro.
Why You Should Update Immediately
The presence of “zero-click” Remote Code Execution (RCE) flaws in the Android System makes this an essential, non-skippable update. Users are strongly advised to download and install this firmware as soon as it becomes available. Navigate to Settings > About Phone > System updates (or tap the HyperOS logo) to manually check if the OTA patch is ready for your device. As always, ensure your device is charged to at least 50% and connected to a stable Wi-Fi network before initiating the installation process.
To track live updates on when Xiaomi’s September 2026 security patch will arrive on your device and to stay informed on the latest developments, you can visit live security patch tracker page. Furthermore, if you prefer not to wait for the regional OTA rollout, you can use our custom-developed MemeOS Enhancer app to download the latest firmware version for your device early, ensuring your phone is fully secured without any delay.
so you telling me POCO F9 Pro and Ultra and F7 Ultra getting HyperOS 4 already while POCO F8 Ultra and Pro are dieing
gotcha
anyone wanna buy my F8 Ultra
lmao